AI Privacy Compliance Roadmap: How AI Providers Comply with Swiss FADP and EU GDPR
A step-by-step implementation blueprint for machine learning developers, SaaS vendors, and enterprise technology leaders navigating simultaneous Swiss nFADP and European Union GDPR mandates.
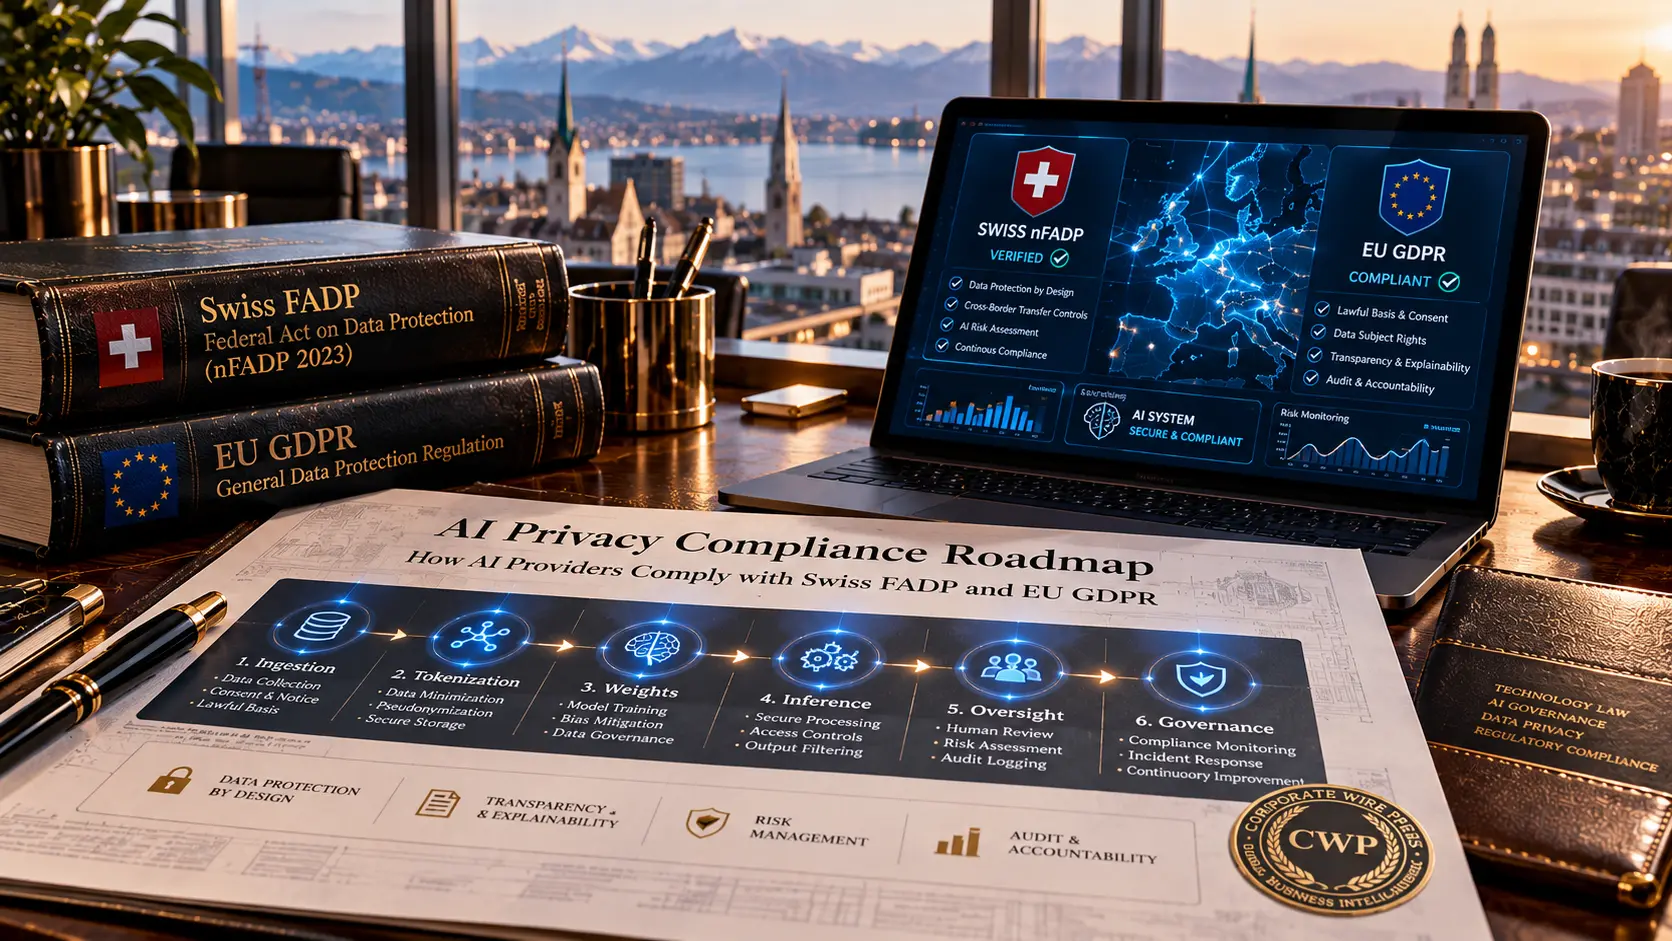
- Lifecycle Compliance Architecture: Achieving simultaneous Swiss nFADP and EU GDPR compliance requires embedding privacy engineering across every machine learning phase: data ingestion, tokenization, model fine-tuning, inference serving, and prompt telemetry.
- Data Ingestion Hygiene: Ingesting web-scraped corpora into foundation models requires establishing lawful processing under GDPR Article 6(1)(f) (Legitimate Interests) while upholding Swiss nFADP Article 6 principles of proportionality and good faith.
- Zero-Data Retention (ZDR) APIs: Enterprise AI SaaS providers must configure default inference endpoints with strict zero-data retention covenants, ensuring enterprise prompts are never recycled into foundation model retraining cycles.
- Explainability & Human-in-the-Loop: Deploying automated decision-making engines in Switzerland and the EEA demands auditable user interfaces that disclose algorithmic parameters and maintain an accessible escalation path to human review.
- Sovereign Transfer Controls: International GPU cloud data flows require executing European Commission Standard Contractual Clauses (SCCs) bolstered by the mandatory Swiss Jurisdictional Addendum and verified Swiss-U.S. Data Privacy Framework certifications.
Executive Blueprint: Navigating the Lifecycle of Dual AI Privacy Compliance
For artificial intelligence providers, machine learning software developers, and cloud SaaS platforms, regulatory compliance cannot be treated as a post-deployment legal afterthought. Contemporary AI architectures are fundamentally data-hungry: they ingest massive corpora during pre-training, fine-tune models on domain-specific user interactions, process real-time personal context through Retrieval-Augmented Generation (RAG) pipelines, and generate probabilistic outputs that directly influence individuals’ professional, financial, and legal outcomes.
Operating across the Swiss-European corridor means building systems that simultaneously satisfy the European Union’s General Data Protection Regulation (Regulation (EU) 2016/679, "GDPR") and Switzerland’s revised Federal Act on Data Protection (revised FADP or "nFADP", SR 235.1). While GDPR compliance addresses approximately 85% of Swiss statutory obligations, failure to bridge the remaining 15% leaves technology executives personally exposed to Swiss criminal fines under Articles 60–66 nFADP and renders enterprise contracts voidable.
This operational roadmap establishes a pragmatic, end-to-end implementation framework. By breaking the compliance journey into distinct engineering and governance phases, AI providers can build audit-proof machine learning services that thrive across Swiss, European, and global enterprise markets.
Phase 1: Pre-Training Data Ingestion & Corpus Hygiene (Web Scraping, Legal Grounds & Provenance)
The initial phase of any AI lifecycle involves data acquisition. Whether training proprietary foundation models or fine-tuning open-source models (such as Llama, Mistral, or specialized domain transformers), developers face immediate data protection exposure.
Under EU GDPR Article 6, every byte of personal data ingested must be grounded in an explicit legal basis. In practice, commercial AI labs rely on "Legitimate Interests" (Article 6(1)(f) GDPR) for web-scale scraping. However, European data protection authorities (such as the CNIL, DPC, and Italian Garante) require developers to conduct and document a rigorous Legitimate Interests Assessment (LIA). This assessment must balance the commercial interest of model development against the fundamental rights of data subjects, proving that the training corpus has been scrubbed of illicit, copyrighted, or sensitive personal data.
Under Swiss nFADP Article 6, the legal framework is principle-based: private processing is lawful unless it breaches personality rights without justification. However, Swiss law strictly enforces the principles of purpose limitation (Zweckbindung) and proportionality (Verhältnismässigkeit). Scraping personal data from public websites without adequate filters or processing data against the recognizable will of the data subject (e.g., ignoring robots.txt disallow directives or scraping behind authentication firewalls) constitutes an unlawful personality infringement under Swiss Civil Code Article 28 and nFADP Article 30.
Actionable Data Ingestion Protocols:
1. Implement Automated PII Scrubbing: Deploy named-entity recognition (NER) filters and regex scrubbing pipelines before tokenization to strip social security numbers, credit card data, email addresses, and phone numbers; 2. Exclude Sensitive Personal Data: Purge all data relating to health, religious beliefs, political views, genetic markers, biometric identifiers, and administrative/criminal proceedings (Article 5(c) nFADP / Article 9 GDPR); 3. Maintain Provenance Registries: Maintain an immutable metadata ledger documenting data origins, licensing agreements, scraping timestamps, and robots.txt compliance to satisfy RoPA obligations (Article 12 nFADP / Article 30 GDPR).
Phase 2: Algorithmic Architecture & Model Fine-Tuning (Privacy by Design & Sensitive Data Isolation)
During the model architecture and fine-tuning phase, machine learning engineers must operationalize Privacy by Design and Privacy by Default (Article 7 nFADP / Article 25 GDPR). Once personal data is encoded into neural network weights, deleting specific data points—the "right to be forgotten" under GDPR Article 17 and Swiss nFADP Article 32—becomes a formidable mathematical challenge, as catastrophic forgetting and model retraining costs make selective unlearning economically prohibitive.
To mitigate this structural risk, forward-thinking AI providers decouple model weights from mutable personal datasets by relying on Retrieval-Augmented Generation (RAG) rather than fine-tuning models on raw customer personal data. In a RAG architecture, the core foundation model remains an immutable, generalized semantic engine, while personal enterprise documents reside within securely partitioned, encrypted vector databases where records can be updated, rectified, or purged on demand.
Technical Safeguards for Model Fine-Tuning:
• Differential Privacy Training: Utilize Differentially Private Stochastic Gradient Descent (DP-SGD) during fine-tuning. By clipping gradients and injecting calibrated mathematical noise, DP-SGD ensures that no single training sample can be reconstructed or extracted via model inversion attacks; • Synthetic Data Substitution: Wherever possible, replace historical customer datasets with high-fidelity synthetic tabular or conversational data generated through generative adversarial pipelines; • Isolated Parameter-Efficient Fine-Tuning (PEFT): Utilize Low-Rank Adaptation (LoRA) or prefix-tuning adapters that isolate enterprise customer weights into modular, disposable adapter files that can be instantly revoked without retraining base models.
Phase 3: Inference, Prompt Telemetry & Zero-Data Retention (ZDR) APIs
When AI applications transition to live customer inference, data processing shifts from model developers to customer interactions. At this stage, B2B SaaS buyers demand ironclad guarantees that proprietary corporate inputs and customer personal data will not be exposed to unauthorized parties or used to train public models.
Under Swiss nFADP Article 8 and GDPR Article 28, AI providers operating as "data processors" must execute formal Data Processing Agreements (DPAs). These contracts must explicitly restrict the provider from processing customer prompt data for any purpose other than providing the immediate inference service requested.
Crucially, AI providers must engineer Zero-Data Retention (ZDR) into their API architecture:
1. Ephemeral Inference Processing: Prompts, system instructions, and generated completions must be processed entirely in volatile GPU RAM and purged immediately upon socket termination; 2. Disabling Foundation Retraining: Default enterprise terms must contractually and technically guarantee that customer prompts will never be harvested for foundational re-training or human review evaluation loops; 3. Ephemeral Cache Management: When implementing semantic prompt caching to reduce latency, all cache stores must be encrypted at rest with customer-managed keys (CMEK) and enforce strict time-to-live (TTL) expiration schedules.
Phase 4: User-Facing Explainability, Automated Decisions & Human Oversight Workflows
Both Swiss nFADP (Article 21) and EU GDPR (Article 22) mandate that individuals subject to automated decision-making must be informed of the automated processing and provided with clear avenues for recourse.
If an AI platform performs automated scoring, classification, or filtering that produces legal or significantly similar effects (e.g., algorithmic credit checks, automated employment applicant ranking, fraud flags, or automated insurance risk premiums), the user interface must incorporate dedicated explainability and human escalation loops.
UX Design Requirements for Algorithmic Transparency:
• Affirmative Automated Decision Notice: Present clear, visible UI disclaimers informing users whenever a decision is rendered by an automated algorithm (e.g., "This preliminary evaluation was calculated automatically by our machine learning scoring engine."); • Factor-Level Explainability Dashboards: Display intuitive feature importance breakdowns showing the primary input variables and relative weights that influenced the score (e.g., utilizing SHAP or LIME explainability metrics); • Integrated Human Escalation Request: Provide an unhindered, visible button or form allowing data subjects to challenge the automated outcome and request formal review by a qualified human being (Überprüfung durch eine natürliche Person pursuant to Art. 21(2) nFADP);; • Human Oversight SLA: Establish internal operational protocols ensuring that escalated automated decisions are reviewed and resolved by a human operator within a guaranteed business timeframe (typically 5 to 10 business days).
Phase 5: Cross-Border GPU Infrastructure, Cloud Transfers & Sovereign Isolation
Because high-performance GPU infrastructure is geographically concentrated in specialized hyperscaler data centers across Frankfurt, Zurich, Dublin, and the United States, AI platforms routinely transfer data across international borders.
To maintain cross-border compliance under Swiss nFADP Article 16 and GDPR Articles 44–46, AI providers must execute a structured data transfer architecture:
1. Intra-European & Swiss Hosting: The most defensible operational posture is to maintain sovereign European hosting. The European Commission formally recognizes Switzerland as providing adequate data protection (adequacy renewed in January 2024), and the Swiss Federal Council recognizes all EU/EEA states as adequate. Hosting AI inference within EU and Swiss data centers eliminates cross-border legal friction; 2. Standard Contractual Clauses with the Swiss Addendum: When routing inference traffic or fine-tuning workflows to servers outside the EEA and Switzerland (e.g., to GPU clusters in the United States, Canada, or the UK), providers must execute the European Commission’s Modular Standard Contractual Clauses (SCCs) augmented with the mandatory Swiss Jurisdictional Addendum issued by the Federal Data Protection and Information Commissioner (FODPC); 3. Swiss-U.S. Data Privacy Framework: In September 2024, the Swiss-U.S. Data Privacy Framework officially entered into force. Swiss AI providers transferring data to U.S. cloud providers can rely on this framework, provided the U.S. receiving entity maintains an active, public certification with the U.S. Department of Commerce.
Phase 6: Governance, Continuous DPIAs & Mitigating Executive Criminal Liability
The final phase of the compliance roadmap institutionalizes long-term governance, risk assessment, and executive liability protection.
Unlike the EU GDPR—which penalizes corporate balance sheets with administrative turnover fines—the Swiss nFADP imposes direct criminal fines of up to CHF 250,000 on individual corporate decision-makers (directors, C-suite officers, and designated managers) who intentionally violate statutory transparency, cross-border transfer, or disclosure duties (Articles 60–66 nFADP).
To insulate executive leadership and guarantee institutional defensibility, AI providers must execute three governance pillars:
• Execute Continuous AI DPIAs: Before launching any generative AI service, multimodal computer vision tool, or behavioral scoring engine, conduct a comprehensive Data Protection Impact Assessment (Article 22 nFADP / Article 35 GDPR). Document technical model parameters, bias mitigation strategies, and adversarial testing results; • Appoint a Data Protection Advisor (Datenschutzberater): Appoint an independent internal or external privacy advisor pursuant to Article 10 nFADP. Under Article 23(4) nFADP, consulting this advisor on high-risk DPIAs legally exempts private controllers from having to submit the assessment to the Federal Data Protection and Information Commissioner (FODPC); • Comprehensive Employee & Contractor Training: Conduct mandatory training for engineering and product leads regarding Swiss criminal liability standards, establishing clear audit trails that demonstrate good faith and eliminate any presumption of intentional statutory evasion (Vorsatz).
Comprehensive Implementation Matrix: Five-Phase AI Privacy Engineering Roadmap
The following reference matrix synthesizes the end-to-end compliance roadmap across engineering, product design, and corporate governance disciplines.
| Lifecycle Stage | Core Engineering & Legal Deliverable | Primary Technical Constraint | Governing Statutory Mandate |
|---|---|---|---|
| Phase 1: Ingestion | Training Corpus Scrubbing & Provenance Ledger | Deploy NER filtering; purge sensitive categories and criminal data. | Art. 6 nFADP / Art. 6(1)(f) GDPR |
| Phase 2: Fine-Tuning | Privacy by Design & RAG Architecture | Implement DP-SGD; isolate mutable enterprise records in vector stores. | Art. 7 nFADP / Art. 25 GDPR |
| Phase 3: Inference | Zero-Data Retention (ZDR) API Configuration | Process prompts in ephemeral GPU RAM; disable foundational re-training. | Art. 8 nFADP / Art. 28 GDPR |
| Phase 4: Interface | Explainability & Human Review Escalation | Disclose automated decision logic; deploy one-click human review. | Art. 21 nFADP / Art. 22 GDPR |
| Phase 5: Cloud Transfers | GPU Transfer Safeguards & Swiss Addendum | Execute EU SCCs with Swiss Annex; verify Swiss-U.S. DPF certifications. | Art. 16 nFADP / Arts. 44–46 GDPR |
| Phase 6: Governance | AI DPIA & Data Protection Advisor Appointment | Conduct algorithmic risk assessment; secure FODPC consultation relief. | Arts. 10, 22 nFADP / Arts. 35, 37 GDPR |
Frequently Asked Questions: AI Provider Compliance Under Swiss FADP & EU GDPR
The following questions represent the most urgent operational issues raised by enterprise AI startups, cloud vendors, and machine learning architects.
1. Can AI providers legally train foundational models on enterprise customer prompt data in Switzerland or the EU?
Generally, no—unless explicit, informed, and unbundled consent is obtained from both the corporate customer and all affected individual data subjects. Under both GDPR Article 28 and Swiss nFADP Article 8, data processors are legally prohibited from processing customer personal data for their own commercial secondary purposes (such as foundation model retraining). Enterprise AI providers must offer strict Zero-Data Retention (ZDR) commitments.
2. What is the primary operational benefit of appointing a Swiss Data Protection Advisor?
Under Article 23(4) nFADP, if an AI company conducts a Data Protection Impact Assessment (DPIA) that reveals residual high risks, it is normally required to consult the Swiss Federal Commissioner (FODPC), which can delay product launches. However, if the company has appointed an independent Data Protection Advisor (Datenschutzberater) pursuant to Article 10 nFADP and consulted them, the mandatory FODPC consultation is completely waived.
3. How can an AI provider satisfy "the right to be forgotten" when data is embedded in neural network weights?
Because extracting individual training samples from deep neural weights is mathematically complex, the recognized industry and regulatory best practice is architectural: sanitize training corpora prior to pre-training, apply differential privacy (DP-SGD) to prevent memorization, and utilize Retrieval-Augmented Generation (RAG) where personal data resides in editable vector databases rather than fixed model weights.
4. Are AI data transfers from Switzerland to the United States permitted under the Swiss-U.S. Data Privacy Framework?
Yes. The Swiss-U.S. Data Privacy Framework officially entered into force in September 2024. Swiss AI providers transferring data to U.S. cloud GPU hosts or SaaS vendors can rely on this adequacy mechanism, provided the U.S. recipient has formally self-certified under the Swiss-U.S. DPF program with the U.S. Department of Commerce.
Conclusion: Building Trustworthy, Audit-Ready AI Architectures
Navigating dual Swiss nFADP and EU GDPR compliance is not an insurmountable technical hurdle; it is an engineering discipline. By replacing fragmented legal reviews with an integrated compliance roadmap—spanning pre-training corpus scrubbing, Privacy by Design architecture, Zero-Data Retention inference APIs, transparent explainability interfaces, and sovereign GPU infrastructure—technology providers can operate with total regulatory confidence.
In an enterprise software landscape increasingly dominated by security-conscious enterprise buyers, proactive compliance represents a powerful competitive advantage. AI innovators who master the nuances of Swiss and European privacy jurisprudence will establish the trusted foundation necessary to lead the global artificial intelligence economy.
Julian Vance has spent 18 years counseling Fortune 500 AI platforms and multinational financial groups on compliance with Swiss FADP, EU GDPR, and cross-border data transfer mechanisms.
Further Recommended Readings from Our Desks
Swiss FADP vs. EU GDPR: Core Legal Differences, Principles & Requirements Explained
A foundational legal analysis examining the core philosophical doctrines, statutory principles, consent standards, and governance requirements that distinguish Swiss data protection law from the EU GDPR.
Swiss-US Data Privacy Framework vs. EU GDPR: Cross-Border Data Transfers for AI Systems
A technical and regulatory analysis of transatlantic data transfers for artificial intelligence platforms, comparing the Swiss-U.S. Data Privacy Framework with EU GDPR transfer mechanisms, Standard Contractual Clauses, and sovereign cloud infrastructure.
Implications of Swiss Privacy Law & GDPR for AI Companies: Strategy, Risks & Market Access
Strategic analysis for machine learning executives, venture-backed AI labs, and enterprise SaaS providers evaluating jurisdictional advantages, cross-border liabilities, and European market expansion.