Implications of Swiss Privacy Law & GDPR for AI Companies: Strategy, Risks & Market Access
Strategic analysis for machine learning executives, venture-backed AI labs, and enterprise SaaS providers evaluating jurisdictional advantages, cross-border liabilities, and European market expansion.
- Dual-Market Imperative: Modern AI startups cannot isolate Swiss operations from EU markets; extraterritorial reach under GDPR Article 3(2) and Swiss nFADP Article 3 requires a harmonized dual-regime commercial architecture.
- Jurisdictional Arbitrage Fallacy: Relocating AI infrastructure to Switzerland does not insulate a company from EU GDPR if services target EU consumers, but it confers profound institutional stability, IP protection, and banking security.
- B2B Freedom Post-2023: The revised Swiss nFADP eliminated legal entities from data protection scope, transforming Switzerland into an ideal global haven for pure B2B industrial AI, financial knowledge graphs, and corporate analytics.
- Personal Criminal Liability as Corporate Risk: Swiss law targets natural persons (directors, compliance managers) with criminal fines up to CHF 250,000 for intentional non-compliance, altering corporate D&O insurance and executive governance.
- Procurement Gatekeeping: European enterprise buyers increasingly mandate audited proof of both EU GDPR and Swiss nFADP compliance as a strict prerequisite for software licensing and vendor onboarding.
Executive Briefing: The Commercial Reality of Dual Swiss-EU Market Access
For artificial intelligence startups, multinational software vendors, and venture capital investors, evaluating where to incorporate, host, and commercially deploy machine learning services requires mastering the intersection of law, technology, and market strategy. The European continent represents one of the world's most lucrative digital economies, but navigating the dual legal regimes of Switzerland's revised Federal Act on Data Protection (nFADP) and the European Union's General Data Protection Regulation (GDPR) presents both immense opportunities and severe operational pitfalls.
A pervasive myth among early-stage machine learning founders is that establishing operations in Switzerland creates an impenetrable regulatory shield against European Union data privacy enforcement. In reality, modern data privacy laws operate extraterritorially. Under GDPR Article 3(2), any Swiss-based AI provider offering goods or services to individuals in the EU or monitoring their behavior remains fully subject to GDPR enforcement and administrative corporate fines up to €20 million or 4% of worldwide annual turnover.
Conversely, foreign AI providers outside Switzerland that process personal data producing effects within Switzerland are subject to Swiss nFADP jurisdiction pursuant to Article 3 nFADP. Far from being a burden, however, understanding the strategic implications of these overlapping regimes allows innovative AI companies to architect their corporate structure, intellectual property licensing, and cloud topology to maximize enterprise credibility and accelerate enterprise procurement.
Extraterritorial Reach: When Do Both Swiss nFADP and EU GDPR Apply Simultaneously?
Determining which legal regime governs an artificial intelligence platform depends on two statutory tests: the establishment principle and the marketplace effect principle.
1. The EU GDPR Extraterritorial Test (Article 3 GDPR): The GDPR applies to the processing of personal data in the context of the activities of an establishment of a controller or processor in the EU (Article 3(1)). Furthermore, under Article 3(2), it applies to non-EU controllers (including Swiss AI firms) if processing activities are related to offering goods or services to data subjects in the Union or monitoring their behavior within the Union.
2. The Swiss nFADP Extraterritorial Test (Article 3 nFADP): In a parallel approach derived from international private law, Article 3 nFADP codifies the principle of effects (Auswirkungsprinzip). The Swiss statute applies to all matters that produce an effect in Switzerland, even if the processing was initiated abroad. An American or German AI SaaS provider processing Swiss residents' personal data is directly accountable under Swiss law.
The practical result is that virtually every commercial AI product serving European clients must operate under a synchronized dual-compliance framework. The critical differences in liability, corporate governance, and algorithmic oversight cannot be compartmentalized by geography.
Jurisdictional Advantages: Why Global AI Companies Incorporate in Switzerland
Despite extraterritorial regulatory overlap, Switzerland has emerged as a premier global jurisdiction for frontier artificial intelligence labs, autonomous robotics developers, and privacy-preserving machine learning infrastructure.
Key Strategic Advantages of the Swiss Jurisdiction:
• Exclusion of B2B Corporate Data: With the September 1, 2023 enactment of nFADP, Switzerland eliminated legal entities from data protection scope. Industrial AI platforms, automated business-to-business intelligence tools, and corporate data analytics can process institutional data without data privacy constraints;
• World-Class Intellectual Property Protection: Swiss law offers robust protection for algorithmic trade secrets, software patents, and proprietary model weights under the Swiss Federal Act on Unfair Competition (UWG) and the Swiss Patent Act;
• Political and Institutional Neutrality: Switzerland operates outside the European Union’s legislative bureaucracy while maintaining bilateral mutual adequacy. Swiss companies enjoy frictionless data flows with the EEA while remaining insulated from direct EU regulatory directives;
• Premier Research Ecosystem: The presence of world-leading institutions such as ETH Zurich, EPFL, and the Swiss National AI Initiative (SNAI) creates an unparalleled talent pool backed by sovereign computational clusters (such as the Swiss National Supercomputing Centre CSCS).
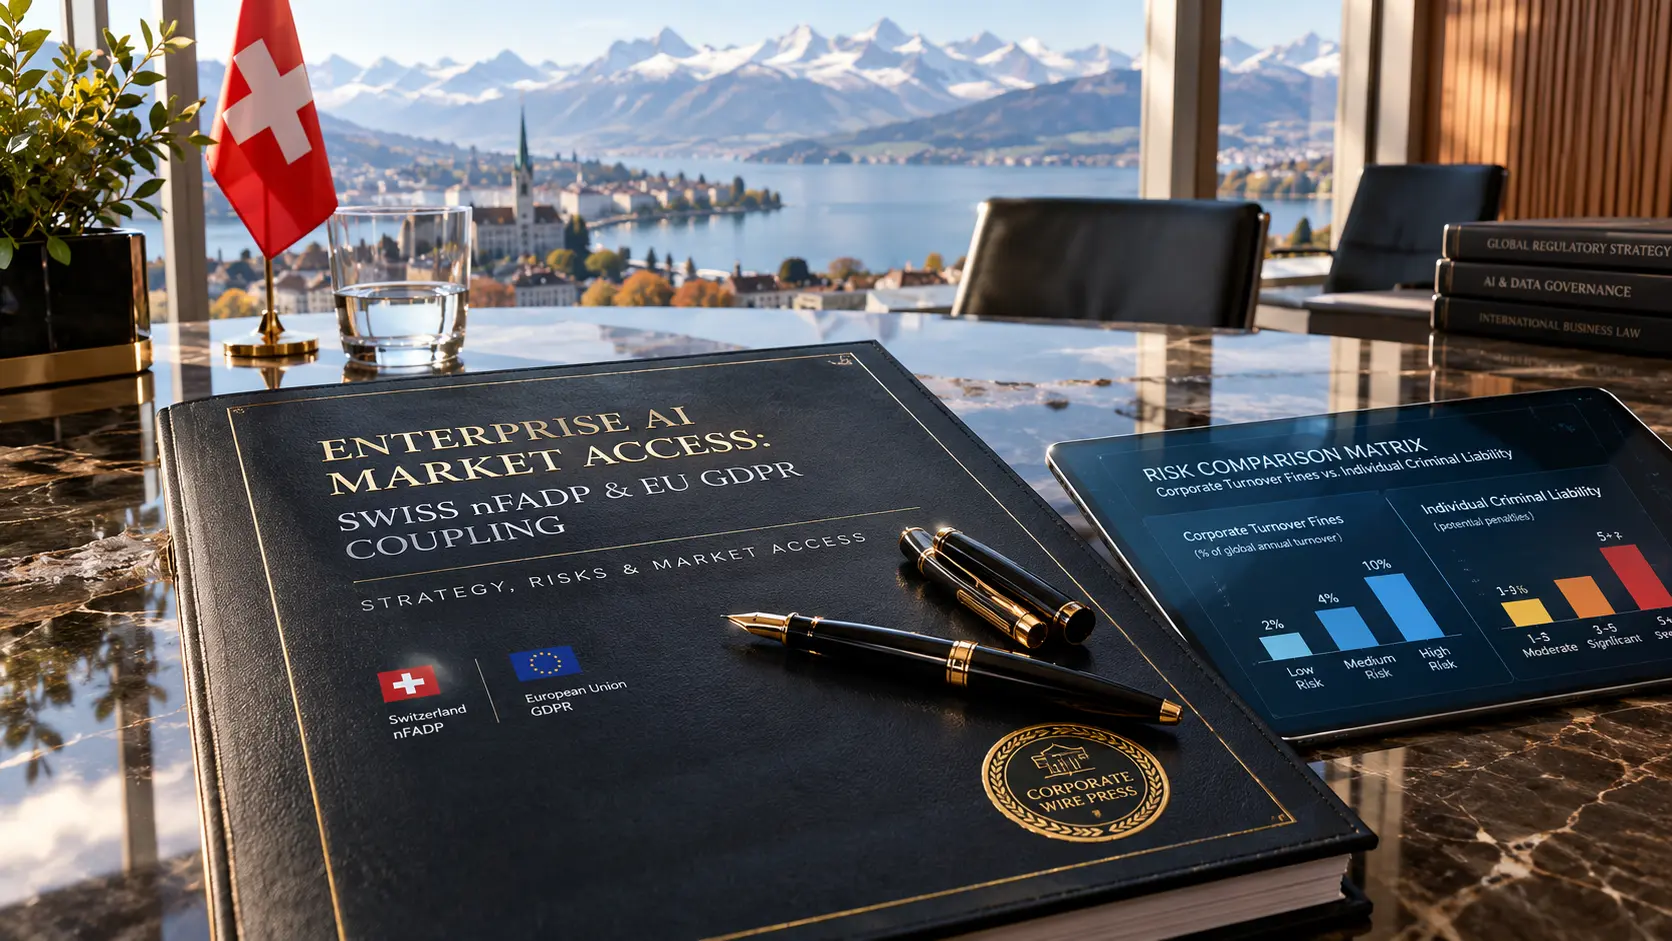
Commercial Risk Matrix: Corporate Turnover Fines vs. Executive Criminal Liability
When evaluating enterprise risk, general counsels and board audit committees must recognize that Swiss nFADP and EU GDPR enforce compliance through fundamentally different punitive architectures.
| Risk Dimension | EU GDPR Regime | Swiss nFADP Regime | Executive & Operational Impact |
|---|---|---|---|
| Primary Target of Fines | Corporate legal entity (the enterprise balance sheet). | Natural persons (individual directors, C-suite officers, managers). | Under Swiss law, executives cannot hide behind corporate limited liability. |
| Maximum Financial Penalty | Up to €20M or 4% of total worldwide annual turnover. | Up to CHF 250,000 per statutory offense. | GDPR threatens corporate solvency; Swiss nFADP threatens personal executive wealth and criminal records. |
| Mental State Required | Strict liability / negligence is sufficient for administrative fines. | Intentional conduct (Vorsatz) is strictly required for criminal penalties. | Simple negligence is not criminally punishable in Switzerland, but willful regulatory defiance is. |
| Enforcement Mechanism | Administrative decisions by national Data Protection Authorities (DPAs). | Criminal prosecution by Cantonal Public Prosecutors (Staatsanwaltschaften). | Swiss investigations involve formal criminal justice proceedings rather than bureaucratic agency fines. |
| Corporate Indemnification | Corporate liability insurance and indemnification are standard. | Corporations are legally restricted from paying criminal fines on behalf of executives. | C-suite officers must secure specialized D&O legal defense coverage under Swiss law. |
Enterprise Procurement Hurdles: How Dual Compliance Accelerates SaaS Sales Cycles
In the enterprise AI software ecosystem, the primary bottleneck to recurring revenue is not customer acquisition—it is passing the rigorous cybersecurity and data privacy vendor review conducted by enterprise procurement and legal departments.
Enterprise procurement directors at Tier-1 Swiss private banks, European pharmaceutical conglomerates, and multinational industrial groups enforce non-negotiable compliance checklists. Presenting an AI solution that only references EU GDPR triggers immediate red flags in Switzerland, particularly regarding:
1. Missing Swiss Jurisdictional Addenda in Standard Contractual Clauses (SCCs); 2. Failure to account for Swiss "High-Risk Profiling" standards under nFADP Article 5(f); 3. Omission of the Swiss Federal Data Protection and Information Commissioner (FODPC) in privacy documentation; 4. Ambiguity regarding whether corporate prompt streams are recycled into public model retraining cycles.
AI providers that proactively package validated Swiss nFADP and EU GDPR compliance dossiers—complete with audited Zero-Data Retention (ZDR) architecture, comprehensive Data Protection Impact Assessments (DPIAs), and executed Swiss SCC Addenda—shorten enterprise procurement review from six months to under three weeks.
Strategic Corporate Structuring: Architecting Sovereign AI Cloud Topologies
To optimize operational efficiency while minimizing cross-border legal friction, multinational AI providers should implement a dual-region infrastructure topology:
• Sovereign Swiss-EU Data Planes: Host production inference clusters within dedicated, sovereign hyperscaler data center regions located in Zurich and Frankfurt. Because Switzerland and the European Union maintain reciprocal adequacy decisions, customer prompt context and vector embeddings flow between these regions without supplemental transfer agreements;
• Strict Separation of Model Weights and Personal Data: Maintain public foundation models as stateless, immutable computing engines while isolating customer personal data within customer-managed, encrypted vector stores (utilizing Retrieval-Augmented Generation RAG);
• Automated Transnational Scrubbing: When routing auxiliary telemetry or anonymized analytics to global corporate headquarters in the United States or Asia, pass all traffic through edge sanitization proxies that strip all natural person identifiers.
Frequently Asked Questions: Strategy & Market Access for AI Companies
The following inquiries represent key commercial and structural questions posed by enterprise technology founders and corporate investors.
1. Does incorporating an AI company in Switzerland protect it from EU GDPR fines?
No. If your Swiss entity offers AI services to customers located in the European Union or monitors the behavior of EU data subjects, you fall squarely under GDPR Article 3(2) extraterritorial jurisdiction. EU data protection authorities can issue cross-border orders and collaborate with Swiss judicial authorities to enforce judgments.
2. Can an AI company process B2B corporate data freely in Switzerland without privacy constraints?
Yes. Since September 1, 2023, the revised Swiss nFADP strictly protects natural persons and excludes legal entities. Provided that enterprise datasets contain no direct human names or identifiable personal markers, B2B company data, financial records, and operational spreadsheets can be processed without triggering Swiss data protection restrictions.
3. What is the business cost of ignoring Swiss compliance for EU-based AI providers?
Beyond potential Swiss criminal liability for company officers under nFADP Articles 60–66, the primary cost is lost market access. Swiss enterprise clients—including major pharmaceutical, banking, and wealth management institutions—are legally required to audit their processors and will immediately disqualify non-compliant software vendors.
4. How do venture capital and private equity investors evaluate dual Swiss-EU compliance during due diligence?
Sophisticated technology investors view dual compliance as proof of enterprise maturity. Clean IP provenance, auditable training data registries, zero-data retention commitments, and dual Swiss-EU privacy documentation eliminate major regulatory liabilities during acquisition or IPO due diligence.
Conclusion: Turning Regulatory Rigor into Commercial Advantage
The global artificial intelligence landscape is rapidly transitioning from unconstrained experimentation to regulated enterprise deployment. Technology providers that view data protection as a defensive chore will continually struggle with regulatory friction, procurement delays, and executive legal exposure.
By strategically embracing both Swiss nFADP and EU GDPR standards, forward-thinking AI companies establish an unassailable commercial reputation. Switzerland’s business-friendly B2B legal framework, combined with seamless European market access, offers an extraordinary launchpad for the next generation of trustworthy, high-performance artificial intelligence innovation.
Julian Vance has spent 18 years counseling Fortune 500 AI platforms and multinational financial groups on compliance with Swiss FADP, EU GDPR, and cross-border data transfer mechanisms.
Further Recommended Readings from Our Desks
Swiss FADP vs. EU GDPR: Core Legal Differences, Principles & Requirements Explained
A foundational legal analysis examining the core philosophical doctrines, statutory principles, consent standards, and governance requirements that distinguish Swiss data protection law from the EU GDPR.
Swiss-US Data Privacy Framework vs. EU GDPR: Cross-Border Data Transfers for AI Systems
A technical and regulatory analysis of transatlantic data transfers for artificial intelligence platforms, comparing the Swiss-U.S. Data Privacy Framework with EU GDPR transfer mechanisms, Standard Contractual Clauses, and sovereign cloud infrastructure.
AI Privacy Compliance Roadmap: How AI Providers Comply with Swiss FADP and EU GDPR
A step-by-step implementation blueprint for machine learning developers, SaaS vendors, and enterprise technology leaders navigating simultaneous Swiss nFADP and European Union GDPR mandates.