Swiss-US Data Privacy Framework vs. EU GDPR: Cross-Border Data Transfers for AI Systems
A technical and regulatory analysis of transatlantic data transfers for artificial intelligence platforms, comparing the Swiss-U.S. Data Privacy Framework with EU GDPR transfer mechanisms, Standard Contractual Clauses, and sovereign cloud infrastructure.
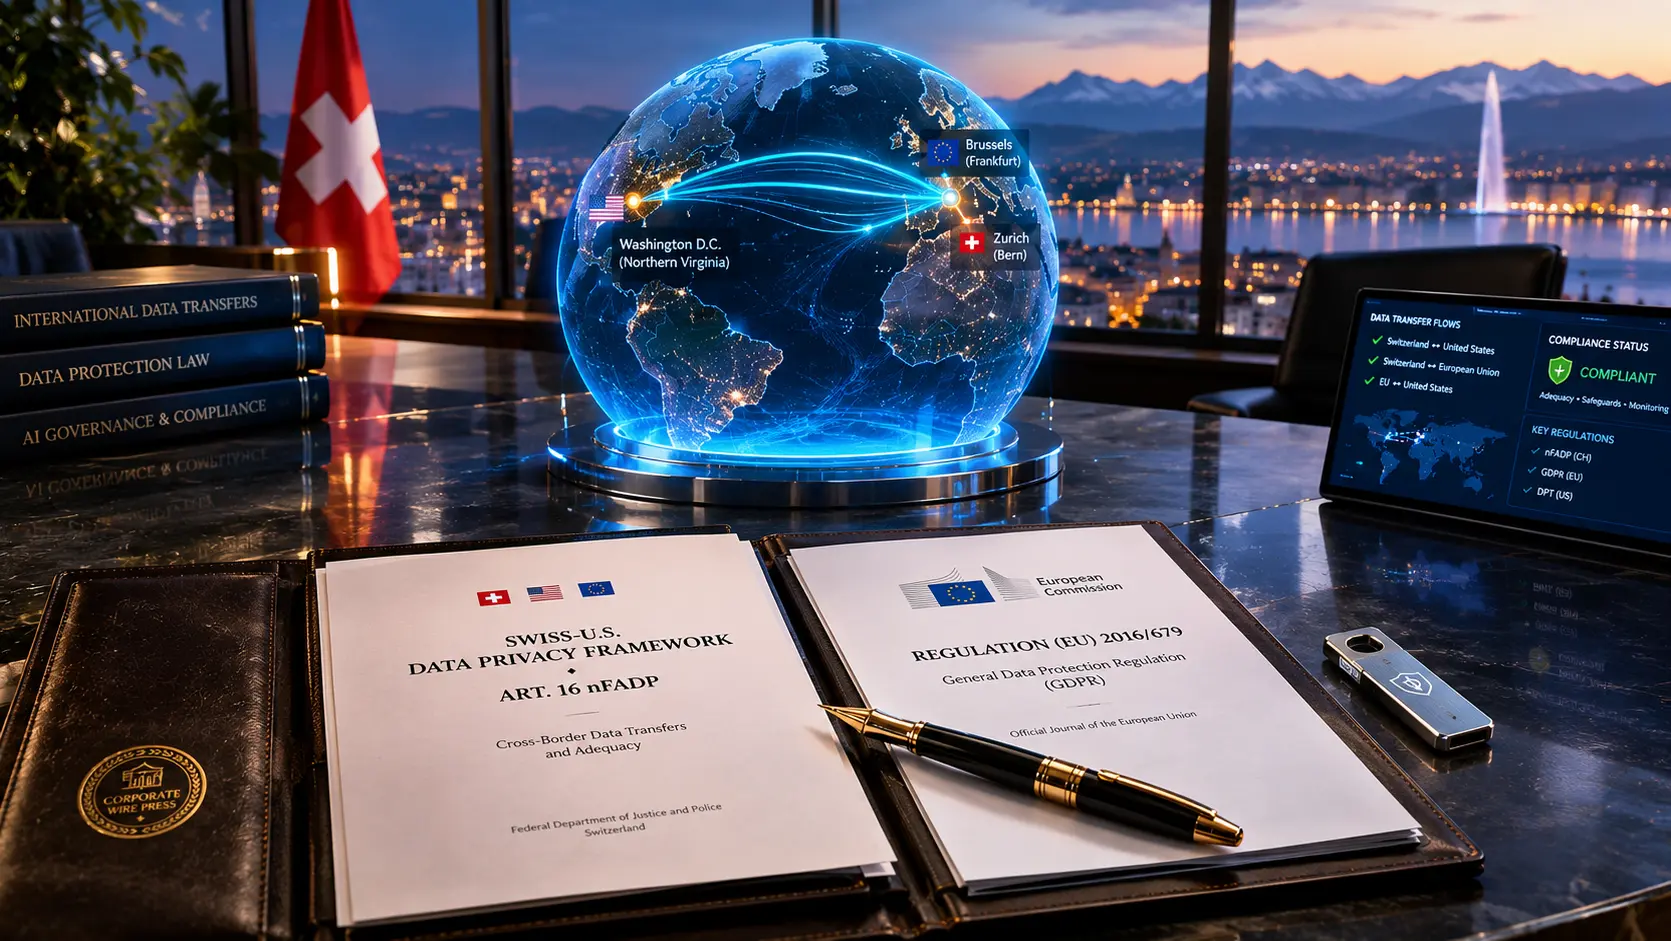
- Statutory Entry into Force: On September 15, 2024, the Swiss-U.S. Data Privacy Framework (Swiss-U.S. DPF) officially entered into force, restoring an adequacy mechanism for commercial data flows between Switzerland and certified U.S. entities.
- Symmetric Architecture: The Swiss-U.S. DPF mirrors the EU-U.S. Data Privacy Framework adopted in July 2023, relying on U.S. Presidential Executive Order 14086 to limit U.S. intelligence access to necessary and proportionate surveillance.
- Distinct Swiss Redress Mechanism: While EU citizens appeal through national DPAs to the U.S. Civil Liberties Protection Officer (CLPO) and Data Protection Review Court (DPRC), Swiss residents submit claims via the Swiss Federal Data Protection and Information Commissioner (FODPC).
- SCCs Still Vital for Specialized AI: Because many niche GPU cloud providers and open-source AI hosting platforms have not self-certified under DPF, European and Swiss AI providers must maintain executed Standard Contractual Clauses (SCCs) with the mandatory Swiss Addendum.
- Transfer Impact Assessments (TIAs) Remain Mandatory: Relying on SCCs for non-DPF cloud compute clusters still legally requires conducting and documenting a rigorous Transfer Impact Assessment evaluating FISA Section 702 exposure.
The Evolution of Transatlantic Data Flows: From Safe Harbor & Privacy Shield to DPF
For more than two decades, the commercial transfer of personal data between Europe, Switzerland, and the United States has been plagued by legal fragility. The invalidation of the International Safe Harbor Privacy Principles in 2015 (Schrems I) and the subsequent invalidation of the EU-U.S. and Swiss-U.S. Privacy Shield frameworks in 2020 (Schrems II) created massive legal uncertainty for technology providers relying on American cloud infrastructure.
Following the Court of Justice of the European Union’s (CJEU) landmark Schrems II ruling, the Swiss Federal Data Protection and Information Commissioner (FODPC / EDÖB) concluded in September 2020 that the Swiss-U.S. Privacy Shield did not provide an adequate level of data protection under Swiss law, citing broad surveillance powers exercised by U.S. intelligence agencies under Section 702 of the Foreign Intelligence Surveillance Act (FISA) and Executive Order 12333, combined with the lack of judicial redress for non-U.S. persons.
For four years, artificial intelligence companies in Switzerland were forced to rely exclusively on complex, risk-laden transfer mechanisms: executing European Commission Standard Contractual Clauses (SCCs) modified with Swiss-specific addenda and conducting onerous Transfer Impact Assessments (TIAs). The official entry into force of the Swiss-U.S. Data Privacy Framework on September 15, 2024, fundamentally altered this compliance landscape.
Statutory Structure: How the Swiss-U.S. Data Privacy Framework Operates
The Swiss-U.S. Data Privacy Framework operates on a dual-track legal architecture: binding commitments codified in U.S. domestic law and a formal adequacy finding issued under Swiss federal law.
1. U.S. Legal Foundations (Executive Order 14086): On October 7, 2022, U.S. President Joe Biden signed Executive Order 14086 on "Enhancing Safeguards for United States Signals Intelligence Activities." This order introduced binding statutory safeguards requiring U.S. intelligence collection to be conducted only following a determination that it is strictly necessary and proportionate to a validated intelligence priority. Furthermore, it established a two-tier redress mechanism accessible to individuals in qualifying states (including Switzerland and EU member states).
2. The Swiss Adequacy Determination (Article 16 nFADP & DPO Annex 1): On August 14, 2024, following detailed bilateral negotiations, the Swiss Federal Council formally recognized that the United States provides adequate data protection for commercial transfers to certified U.S. entities. The Federal Council amended Annex 1 of the Data Protection Ordinance (DPO, SR 235.11), officially recognizing the Swiss-U.S. DPF as legally effective on September 15, 2024.
Swiss-U.S. DPF vs. EU-U.S. DPF: Key Statutory and Operational Distinctions
While the Swiss-U.S. DPF is designed to function symmetrically with the European Union’s framework, several critical institutional and procedural nuances distinguish the two regimes:
| Governance Dimension | Swiss-U.S. Data Privacy Framework | EU-U.S. Data Privacy Framework | Technical & Legal Impact for AI |
|---|---|---|---|
| Governing Treaty / Order | Bilateral Swiss-U.S. Arrangement under EO 14086. | Bilateral EU-U.S. Agreement under EO 14086. | Substantively identical intelligence access limits and proportionality tests. |
| Supervisory Authority | Federal Data Protection and Information Commissioner (FODPC / EDÖB). | European Data Protection Board (EDPB) and national DPAs. | Swiss regulatory inquiries flow through Bern; EU inquiries flow through national regulators. |
| First-Tier Redress Portal | Claims submitted directly through the Swiss FODPC. | Claims submitted through national EU Data Protection Authorities. | Swiss data subjects must utilize Swiss administrative channels for surveillance complaints. |
| Second-Tier Judicial Review | U.S. Data Protection Review Court (DPRC). | U.S. Data Protection Review Court (DPRC). | Both Swiss and EU individuals have equal standing before the independent U.S. review court. |
| Certification Mechanism | Separate Swiss-U.S. DPF self-certification via U.S. Dept of Commerce. | EU-U.S. DPF self-certification via U.S. Dept of Commerce. | U.S. AI cloud vendors must actively opt in to the Swiss module; EU certification alone is insufficient. |
| Arbitration Tribunal | Swiss-U.S. DPF Arbitral Panel. | EU-U.S. DPF Arbitral Panel. | Provides binding arbitration for residual commercial data misuse disputes. |
The Separate Certification Trap: Why EU-U.S. Certification Does Not Cover Switzerland
One of the most dangerous operational traps confronting European and Swiss artificial intelligence companies is the "Single Certification Assumption."
A significant number of American AI tool providers, vector database startups, and GPU cloud platforms have completed their self-certification under the EU-U.S. Data Privacy Framework with the U.S. Department of Commerce. However, the Swiss-U.S. DPF is an entirely separate legal instrument that requires an explicit, separate opt-in certification.
If a Swiss AI company transfers personal data (such as prompt inputs, customer embeddings, or user metadata) to a U.S. cloud host that is certified only under the EU-U.S. DPF but has failed to check the box for the Swiss-U.S. DPF, that cross-border transfer is unlawful under Article 16 nFADP.
Before transferring data to any U.S. machine learning infrastructure provider, compliance teams must verify on the official U.S. Department of Commerce DPF List (dataprivacyframework.gov) that the vendor explicitly maintains an active certification under the "Swiss-U.S. Data Privacy Framework."
Technical Safeguards for Cross-Border GPU Routing & Sovereign AI Enclaves
To ensure absolute regulatory defensibility, advanced AI architectures implement technical isolation measures that neutralize foreign surveillance risks:
• Confidential Computing & Sovereign GPU Enclaves: Deploy inference workloads within hardware-enforced trusted execution environments (TEEs), such as NVIDIA H100/H200 Confidential Computing instances, where data remains encrypted in memory during active processing, preventing cloud host administrators or foreign intelligence agencies from inspecting model states;
• Client-Side Encryption with Swiss Key Custody: Enterprise vector indices and retrieval databases must be encrypted utilizing Customer-Managed Encryption Keys (CMEK) stored within Swiss-domiciled hardware security modules (HSMs);
• Synthetic Token Masking: Before sending prompt context to overseas inference clusters, pass queries through an on-premise or sovereign European sanitization proxy that dynamically substitutes real names, dates, and entity identifiers with synthetic placeholder tokens, re-hydrating the prompt only after the completion stream returns.
Frequently Asked Questions: Swiss-U.S. DPF vs. EU GDPR for Artificial Intelligence
The following inquiries represent key operational questions regarding transatlantic artificial intelligence data flows.
1. When did the Swiss-U.S. Data Privacy Framework officially take effect?
The Swiss-U.S. Data Privacy Framework officially entered into force on September 15, 2024, following the Swiss Federal Council’s formal amendment of Annex 1 to the Data Protection Ordinance (DPO) recognizing the United States as providing adequate data protection for certified entities.
2. Is a Transfer Impact Assessment (TIA) required when transferring data to a DPF-certified AI vendor?
No. When transferring data to an entity certified under the Swiss-U.S. DPF, the adequacy decision removes the legal obligation to conduct a case-by-case Transfer Impact Assessment or execute Standard Contractual Clauses, significantly reducing legal overhead.
3. What happens if a U.S. GPU cloud provider is not certified under the Swiss-U.S. DPF?
If the U.S. provider is not certified under the Swiss-U.S. DPF, you cannot transfer Swiss personal data based on adequacy. You must execute European Commission Standard Contractual Clauses (SCCs) modified with the mandatory Swiss Addendum and complete a formal Transfer Impact Assessment with supplementary technical measures (such as robust encryption).
4. Is the Data Privacy Framework vulnerable to future legal challenges (*Schrems III*)?
Yes. European privacy advocacy organizations (including NOYB led by Max Schrems) have signaled intentions to challenge the EU-U.S. DPF before the CJEU. If the CJEU invalidates the EU framework in the future, the Swiss Federal Council would likely re-evaluate the Swiss-U.S. DPF. Prudent AI providers maintain dual-readiness with executed SCCs and sovereign European hosting fallback options.
Conclusion: Architecting Resilient Transatlantic AI Data Pipelines
The enactment of the Swiss-U.S. Data Privacy Framework provides enterprise artificial intelligence companies with much-needed commercial relief, enabling frictionless cross-border data flows with major American technology platforms. However, regulatory resilience requires proactive vigilance.
By verifying separate Swiss-U.S. DPF certifications, executing European Commission Standard Contractual Clauses with Swiss Addenda for non-certified compute providers, and deploying hardware-level confidential computing enclaves, AI innovators can bridge the transatlantic divide while ensuring ironclad compliance with Swiss and European data protection law.
Julian Vance has spent 18 years counseling Fortune 500 AI platforms and multinational financial groups on compliance with Swiss FADP, EU GDPR, and cross-border data transfer mechanisms.
Further Recommended Readings from Our Desks
Swiss FADP vs. EU GDPR: Core Legal Differences, Principles & Requirements Explained
A foundational legal analysis examining the core philosophical doctrines, statutory principles, consent standards, and governance requirements that distinguish Swiss data protection law from the EU GDPR.
Implications of Swiss Privacy Law & GDPR for AI Companies: Strategy, Risks & Market Access
Strategic analysis for machine learning executives, venture-backed AI labs, and enterprise SaaS providers evaluating jurisdictional advantages, cross-border liabilities, and European market expansion.
AI Privacy Compliance Roadmap: How AI Providers Comply with Swiss FADP and EU GDPR
A step-by-step implementation blueprint for machine learning developers, SaaS vendors, and enterprise technology leaders navigating simultaneous Swiss nFADP and European Union GDPR mandates.